North Korean Hackers' $400 Million Crypto Scam Uncovered by US Authorities
The United States Justice Department announced on Thursday that it had successfully seized cloud infrastructure utilized by North Korean hackers in a sophisticated video-call scam that has reportedly stolen over $400 million in cryptocurrency over an 18-month period.
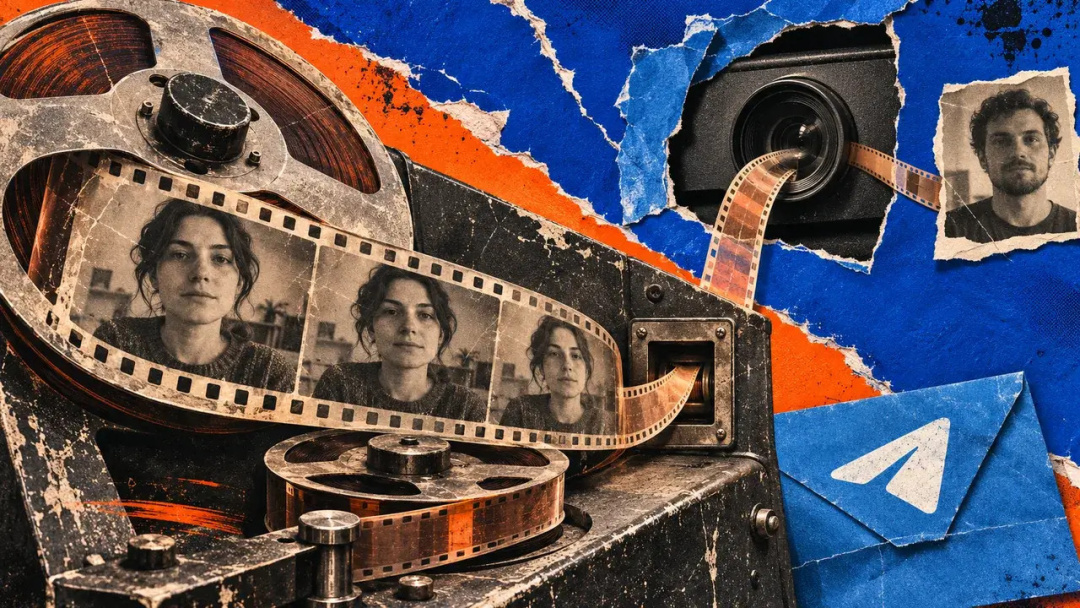
The operation, referred to as "FaceStealer" by the Federal Bureau of Investigation (FBI), involved hackers sending meeting invitations from accounts compromised from previous victims. Once a target joined the call, the hackers would record their webcam video and play a pre-recorded clip featuring a known victim, creating the illusion that trusted contacts were present. The FBI noted that the criminals have begun employing AI-generated deepfakes of well-known figures in the cryptocurrency space to enhance their deception.
Explore on Amazon
Amazon shopping links. As an Amazon Associate I earn from qualifying purchases.
Following the initial contact, the hackers would simulate a technical error and provide a link purportedly to resolve the issue. This link would install malware on the victim's device. In some instances, the hackers waited months or even over a year before executing the theft of funds. They would then leverage the victim's contacts to identify new targets, expanding their fraudulent network.
Most of the victims targeted by this operation were individuals working in the cryptocurrency sector and related internet fields. The FBI has indicated that there is a growing trend of these hackers focusing on open-source software developers, likely to facilitate supply-chain attacks.
FBI's Seizure of Webcam Evidence
Under a federal warrant, the FBI has confiscated over 900 webcam videos of victims, highlighting the extensive reach of this scam. Patrick Grandy, head of the FBI's Los Angeles field office, emphasized the creativity required to avoid falling victim to such schemes, stating, "If you can't imagine a scenario where you might fall prey to it, you are not thinking creatively enough."
The FBI has linked the FaceStealer operation to a hacking group known as Sapphire Sleet or UNC1069, which operates independently from the North Korean military hackers believed to be responsible for the Binance theft. In that incident, the group known as TraderTraitor allegedly stole more than $6 billion around October 29, marking it as one of the largest crypto heists on record. Since then, U.S. agencies and private firms have managed to freeze over $2.7 billion of the stolen funds.
How The Scheme Worked
M. Scott Proctor, the principal deputy assistant attorney general for national security, stated, "North Korea's government bankrolls its rogue regime and illicit weapons program through cryptocurrency theft." Despite these allegations, North Korea has denied any involvement in the Binance hack.
The implications of these actions are significant, as they reveal a complex web of cybercrime that not only affects individual victims but also poses a broader threat to the integrity of the cryptocurrency market. The ongoing investigations and legal actions highlight the challenges authorities face in combating such elaborate schemes.