FBI Warns North Korean Hackers Use Webcam Footage in Crypto Scams
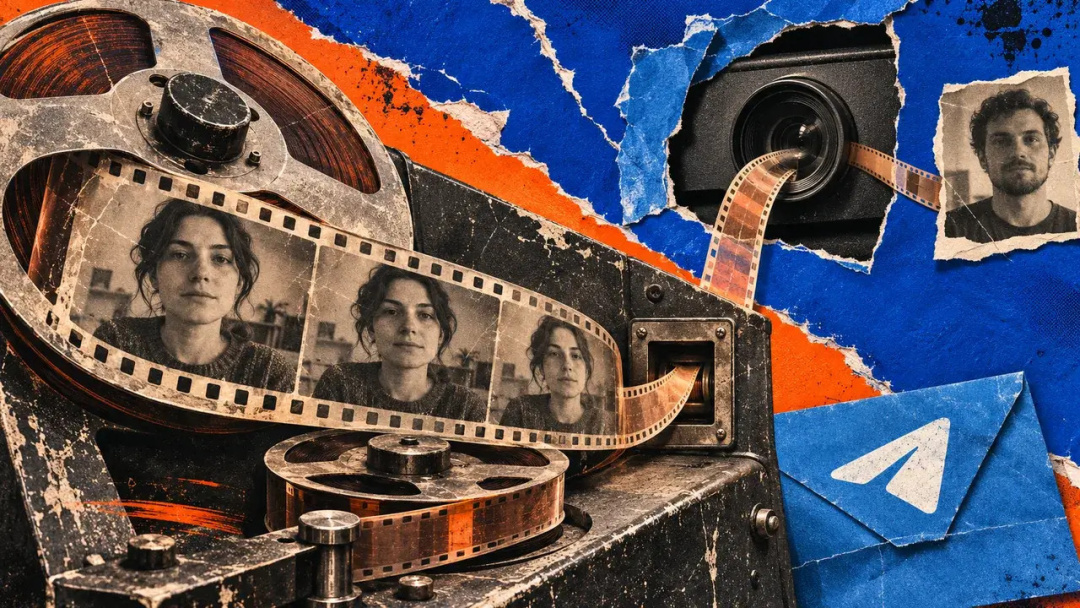
North Korean hackers have devised a cunning scheme that uses stolen webcam recordings to impersonate cryptocurrency workers during fake meetings, effectively turning one victim's familiar face into bait for the next target, according to a warning from the FBI. This alarming tactic has reportedly resulted in over $400 million in cryptocurrency theft over the past 18 months.
On November 12, the Justice Department announced the disruption of the cloud-based infrastructure utilized in this scheme, known as FaceStealer. The FBI revealed that they had seized more than 900 victim webcam videos under a federal warrant, highlighting the scale of the operation.
Explore on Amazon
Amazon shopping links. As an Amazon Associate I earn from qualifying purchases.
The DOJ's release distinguishes FaceStealer from other high-profile thefts, such as the Binance incident, which has been covered extensively in relation to the FBI's investigations and the exchange's asset recovery efforts. In its FLASH advisory, the FBI detailed how attackers gain access to genuine accounts on platforms like Telegram, LinkedIn, Slack, and Discord. By accessing chat histories, they can craft invitations that appear to be part of ongoing conversations, lending a deceptive sense of familiarity to their approach.
Once a meeting is scheduled, the attackers send a malicious link shortly before the call, directing the target to a counterfeit Zoom or Microsoft Teams session that they control. Upon entering, the victim is greeted by a pre-recorded video of a known contact, which is often a recording of a previous victim. This method allows the hackers to simulate multiple participants, creating an illusion of authenticity.
The FBI notes that while FaceStealer primarily relies on genuine stolen videos, it also employs generated deepfakes to further enhance the impersonation. The attack begins when the target clicks on the imposter meeting link, which initiates the recording of their webcam footage. The attackers then use this footage to impersonate the target in future scams.
Techniques Used in the Scam
During the meeting, the impersonator typically claims there is a technical issue, suggesting a fix that involves downloading an update or running a script. Following these instructions can lead to the installation of malware, which may include tools for harvesting browser cookies, logging keystrokes, and maintaining access to the victim's device.
This scheme intricately combines theft and impersonation, as access to the compromised computer can expose sensitive cryptocurrency information and other valuable data. The FBI's advisory emphasizes that the repercussions of such attacks are not always immediate; there have been instances where cryptocurrency theft and account takeovers occurred months or even over a year after the initial compromise. Therefore, a quiet period following a suspicious meeting does not guarantee that a device or account is secure.
The cycle of reuse in these attacks is particularly concerning. The FBI describes a pattern of compromise, account hijacking, and subsequent fake meetings, indicating that the same stolen footage and accounts are often recycled for new victims. This highlights the ongoing risk posed by such schemes, as the attackers continue to exploit their initial gains to lure in more unsuspecting targets.
The Cover Story
To mitigate the risks associated with these scams, the FBI recommends that individuals use the official meeting application with a unique invite code and verify invitations through different communication channels. Additionally, they advise delaying webcam activation until the inviter can be confirmed as a legitimate participant. An apparent technical issue should not prompt anyone to run scripts or paste terminal code presented as a supposed update.
For those who suspect they have been compromised, the FBI suggests securing cryptocurrency in a new wallet created on an unaffected device, safeguarding communication and developer accounts, alerting contacts and employers, and reporting incidents to the IC3 with the keyword FaceStealer. Informing contacts can help disrupt further attempts to exploit stolen accounts and recordings.