FBI Seizes Virtualine: A Bulletproof Host for Criminals
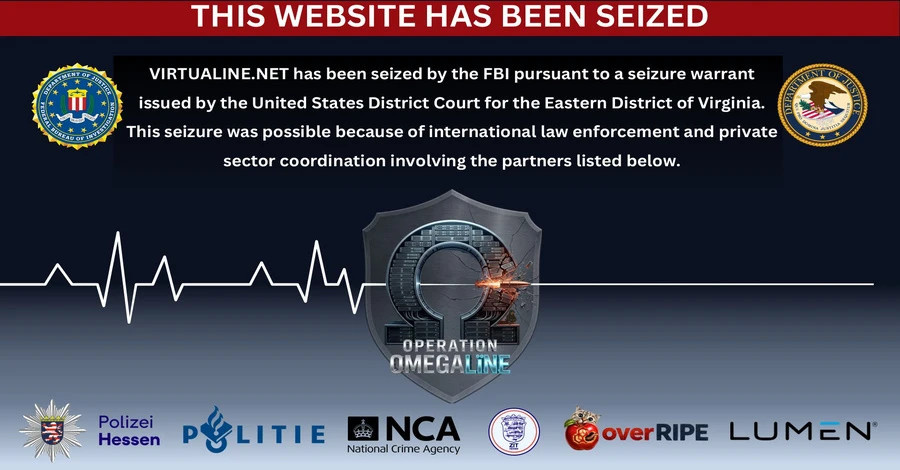
The FBI has seized virtualine.net, the domain of a bulletproof hosting provider that laundered money for its criminal customers and maintained a forum trading in child sexual abuse material, despite repeated warnings from law enforcement and child protection organizations.
The investigation, known as Operation Omegaline, was spearheaded by the FBI's Washington Field Office, with assistance from international partners including Germany’s Polizei Hessen, the Netherlands’ Politie Midden-Nederland, and the UK’s National Crime Agency, as well as private sector collaborators OverRIPE and Lumen.
Explore on Amazon
Amazon shopping links. As an Amazon Associate I earn from qualifying purchases.
Virtualine, which also operated under various aliases such as Secury, Massgod, Spamhouse, Lanedo, and Omegatech, provided hosting services, servers, and domain registrations to clients recruited from cybercrime forums. Prosecutors allege that the service was used to advertise sexually explicit images of minors and disseminate intimate images of both adults and minors without their consent, while also laundering money for its users.
The provider openly courted criminals, stating on the Exploit.in forum in September 2024, "You can use Virtualine for all illegal/black hat activities (including phishing, carding, email spam, port scanning and all others) except for child contents and terrorism activities." In June 2025, it boasted on HackForums that "Virtualine ignored more abuse than your last three therapists."
In March 2026, the company began offering an "additional protection plan" for customers concerned about law enforcement scrutiny. This plan promised to transfer a customer’s criminal infrastructure to another shell company not affiliated with Virtualine upon receiving an official request from law enforcement, effectively reactivating their services elsewhere.
Despite its stated prohibition against child content, Virtualine knowingly hosted a criminal forum identified in court records as Vendor 1, where users could buy and sell explicit images and videos of minors and adults. The forum also advertised hackers for hire who would break into victims’ accounts to steal intimate photos and videos.
International Alerts Ignored by Virtualine
Starting in January 2026, law enforcement agencies in Germany, Canada, and Australia, along with the National Center for Missing and Exploited Children (NCMEC) and a victim’s attorney, alerted the host about child sexual abuse material on the forum’s server. Virtualine, however, continued to keep the forum online and assisted Vendor 1 in establishing a new site for uploading and selling illicit content, which it still hosts.
The Justice Department revealed that Virtualine accepted payments through Bitcoin addresses specifically designed to avoid detection, allowing customers to pay without fear of their funds being flagged as illicit. Blockchain analysis firm Chainalysis, which aided the investigation alongside OverRIPE, found direct links between Virtualine’s payment addresses and ransomware operators, infostealer infrastructure, Russian-language cybercrime forums, and other illicit activities.
Threat intelligence company Silent Push had been monitoring the network since February 11, 2026, when it observed infrastructure transitioning from Railnet, a known bulletproof host, to a newly registered network called Omegatech, where Virtualine Technologies was also discovered.
Following the seizure, Virtualine posted an open letter on a secondary domain, virtualine.org, disputing the allegations and assuring users on Telegram that their data remained secure. The letter's author suggested that they could quickly rebrand and resume operations, indicating a potential for continuity in their illicit activities.
The Unraveling
Despite the seizure, parts of Omegatech’s network are still reachable, although its routing visibility has significantly decreased, a common sign of trouble for operators. Silent Push noted that 50 bulletproof hosting providers have lost their network identifiers in the past year, highlighting the ongoing challenges in combating such services.
A joint advisory issued in November 2025 by CISA, the FBI, the UK’s NCSC, and other agencies warned that bulletproof hosting providers can obtain a new network identifier in just a few business days, allowing them to transfer the same IP ranges and continue their operations with minimal interruption.